Meet Argon. Know your data.
Build your privacy programme.
Personal-data discovery and governance in one workspace, deployed in an environment you control. Explore the actual interface below; every screenshot uses illustrative sample data.
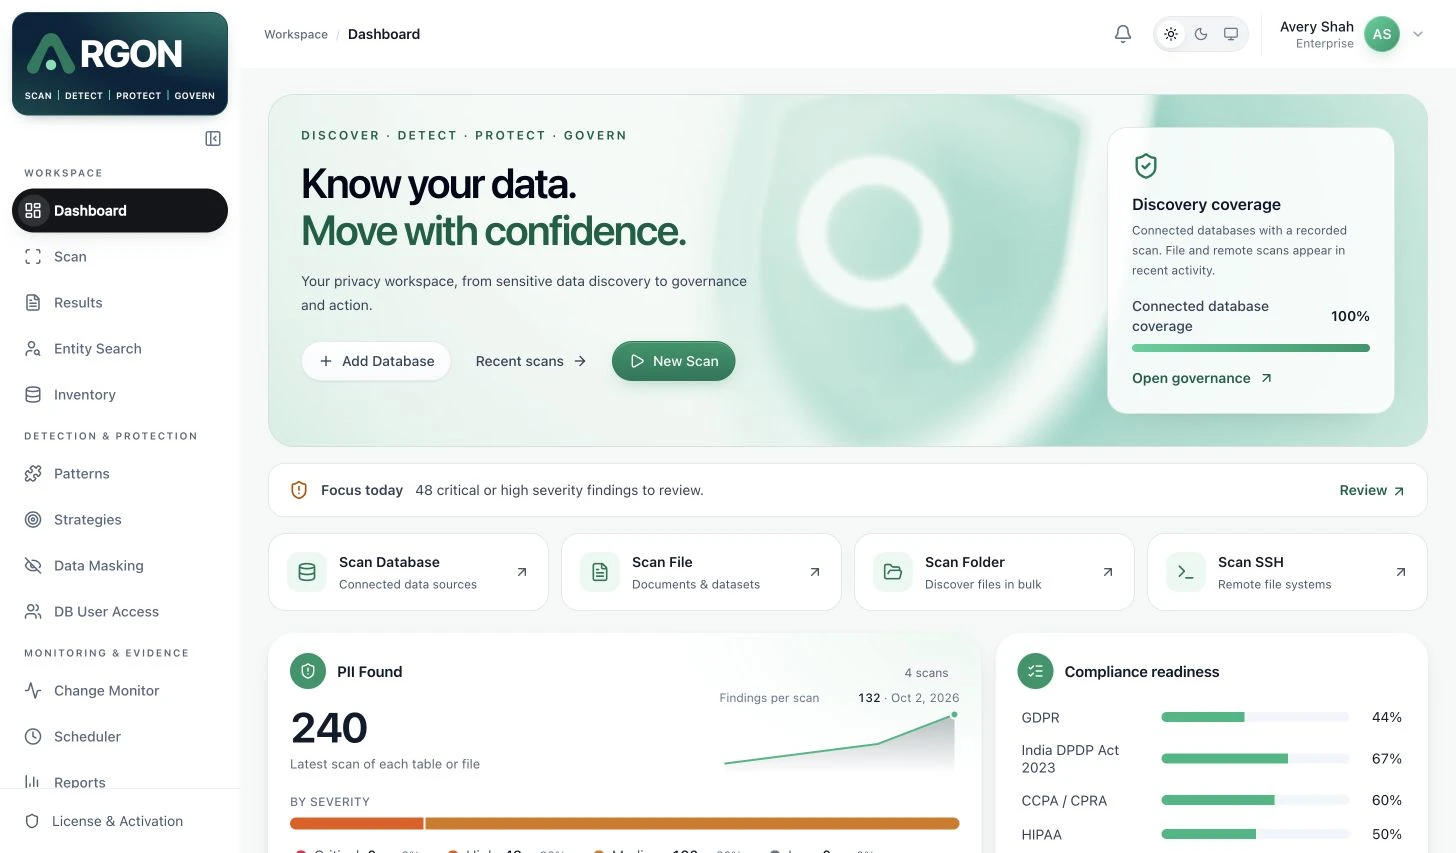
One view of your privacy programme.
Configured sources, scan activity, sensitive-data findings and governance readiness. A working overview that helps your team decide what needs attention next.
- • Connected sources and discovery coverage
- • Finding severity and identifier categories
- • Quick access to database, file, folder and SSH scans
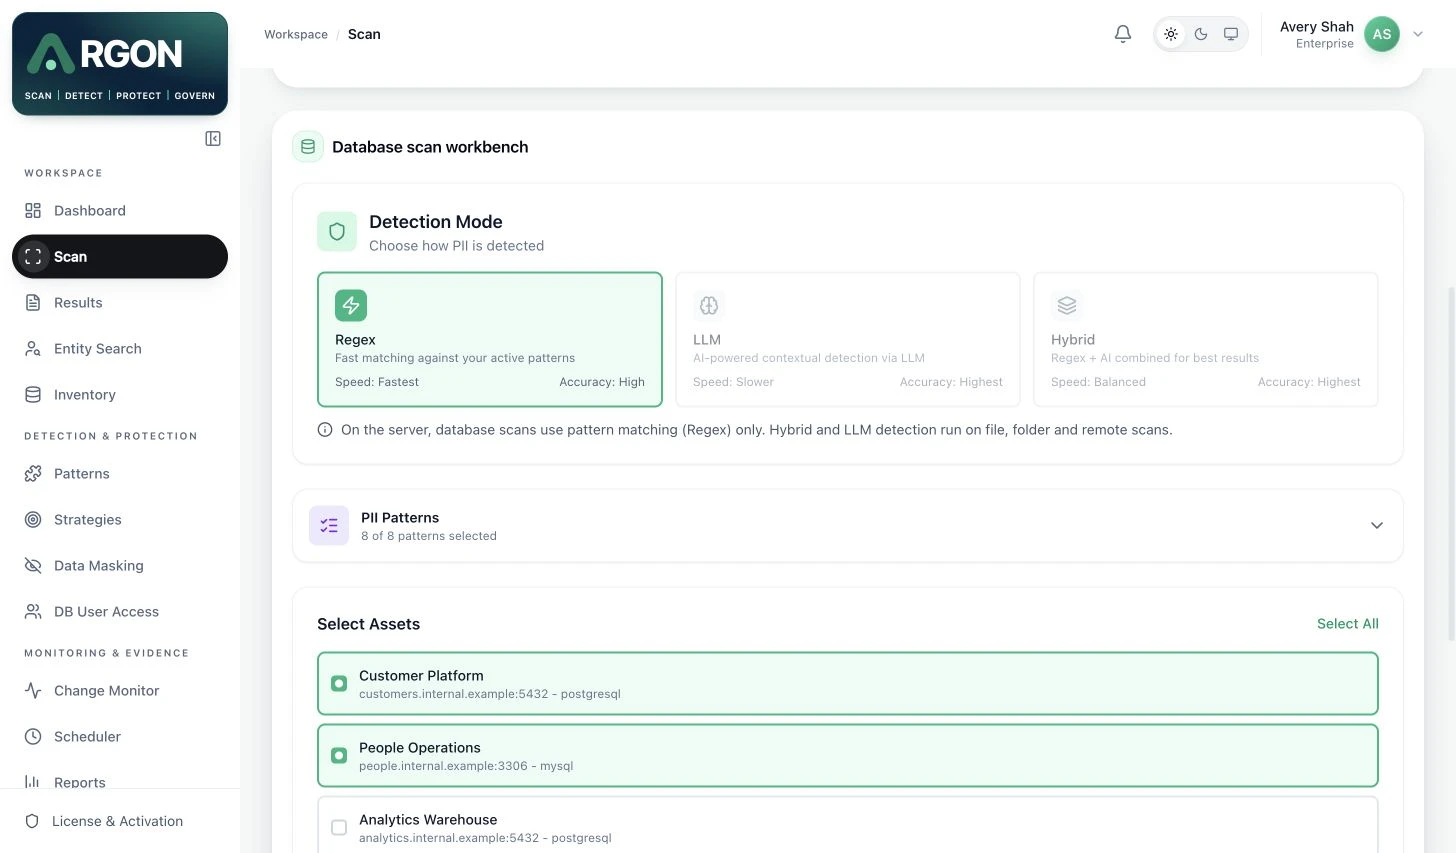
Different sources. One discovery workspace.
Connect your databases, set the scope and launch discovery. File, folder and SSH workflows sit alongside database scanning, with progress visible as a scan runs.
- • Guided source onboarding and focused scope
- • Regex detection; optional AI for supported workflows
- • Progress across database, file, folder and SSH scans
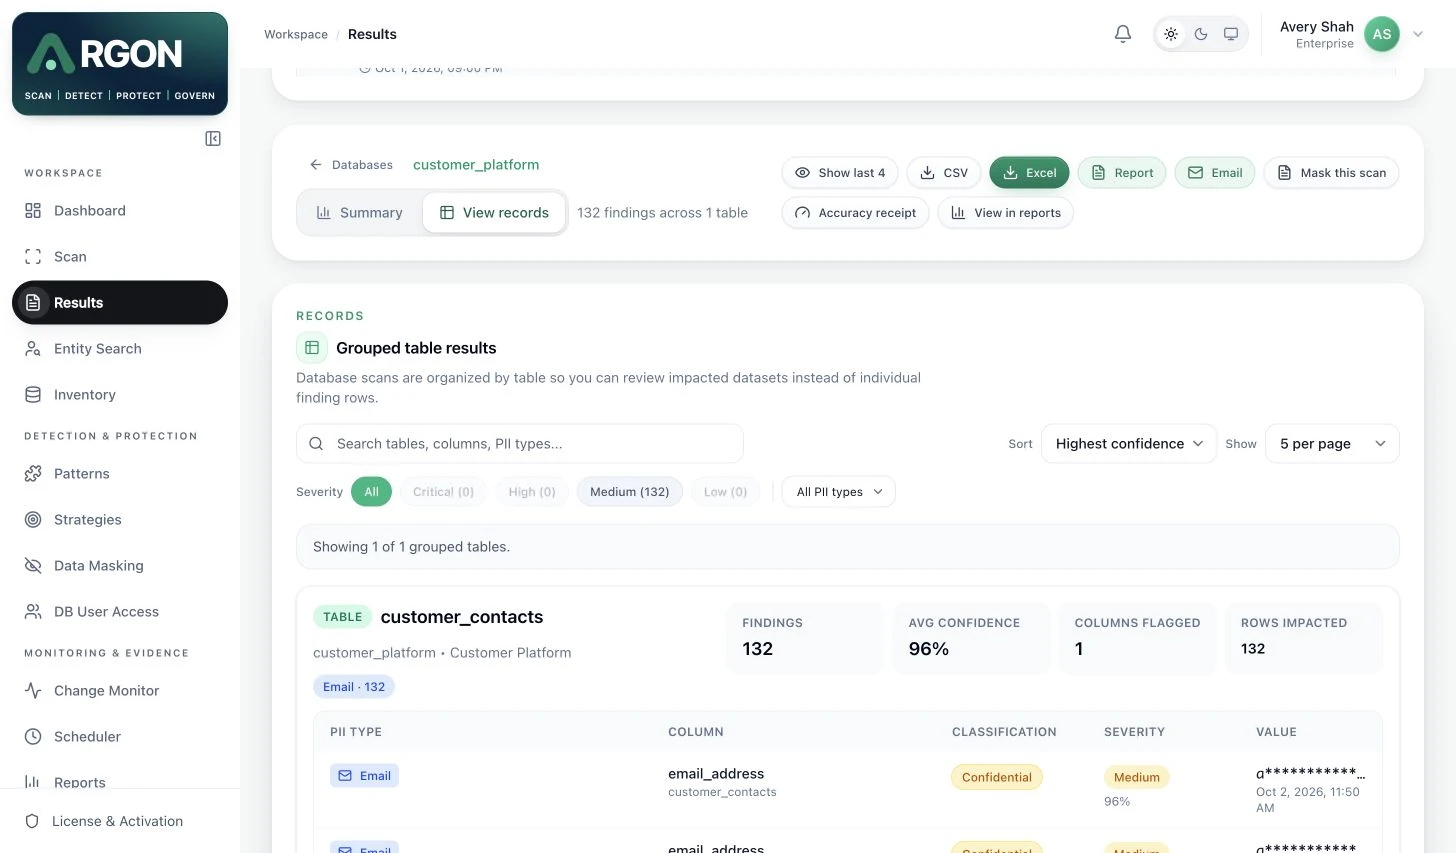
See the finding. Understand the exposure.
Move from scan history to affected databases, tables and columns. Masked samples, severity and confidence give reviewers the context they need to plan the next step.
- • Impact by database, table and column
- • Masked samples with confidence and severity
- • Export and reporting actions beside the findings
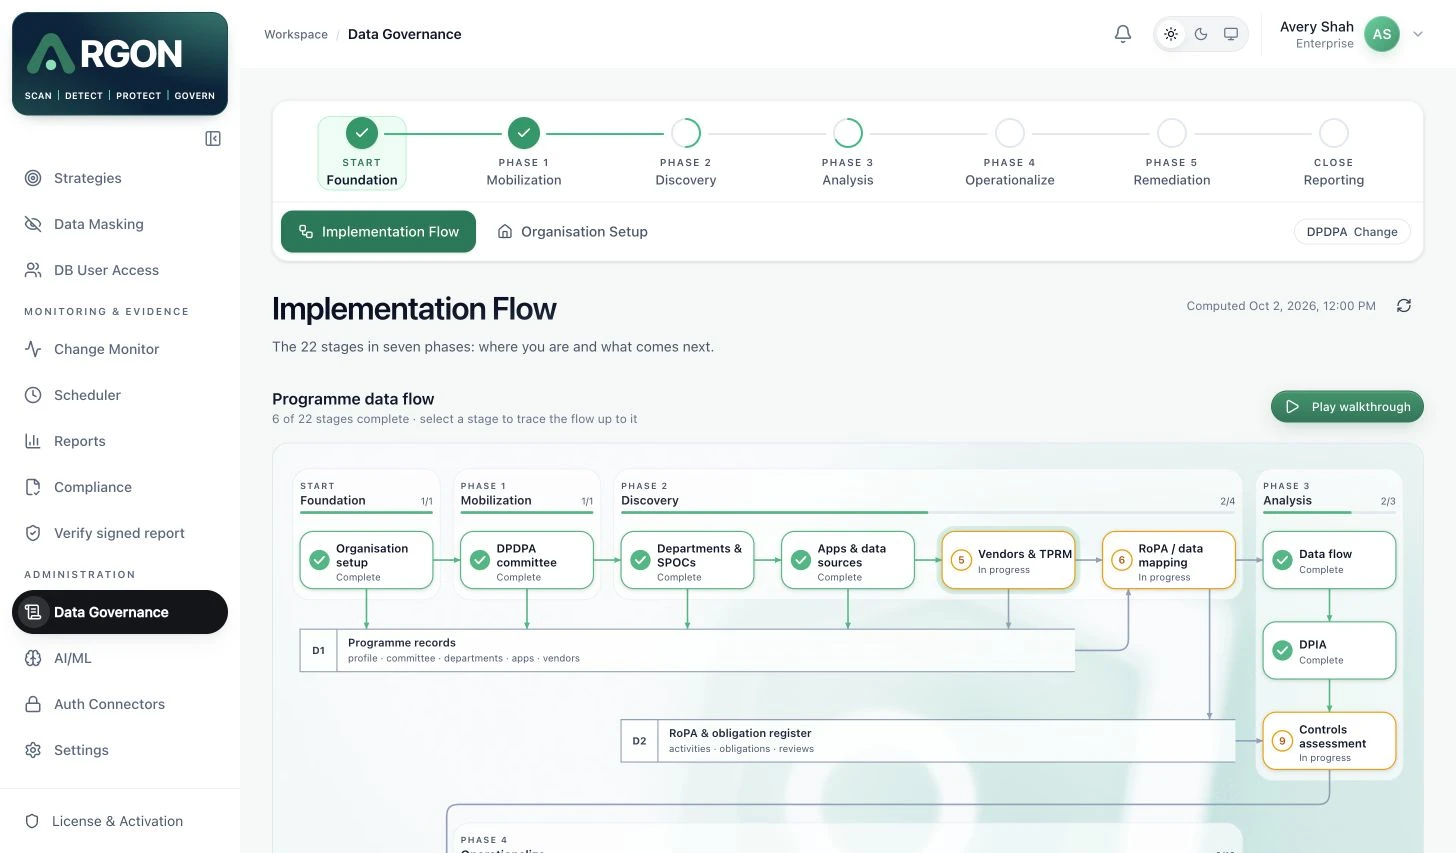
Same phases. The right obligations.
Choose the applicable regulation, then work through a consistent implementation programme. Legal terminology, controls and available options follow the selected framework.
- • A regulation selected before the programme opens
- • 22 stages across seven implementation phases
- • Ownership, controls, gaps and evidence in context
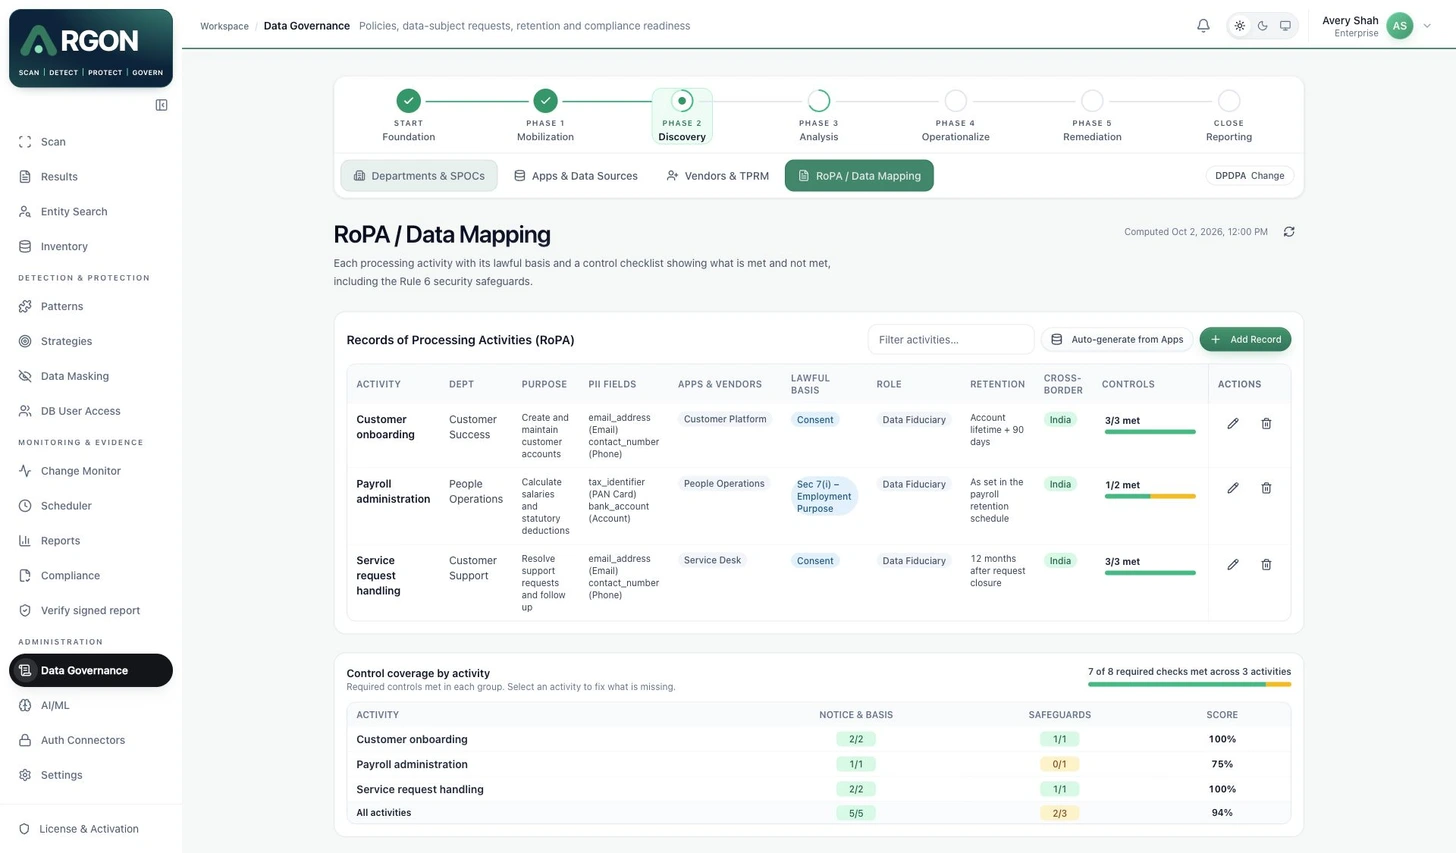
Connect personal data to its purpose.
Record processing activities with accountable departments, lawful basis, systems, retention and control coverage. Keep the business context alongside what your scans find.
- • Activities, departments and source systems
- • Lawful basis and retention recorded together
- • Control coverage for each processing activity
Discovery that fits your environment.
Database, file, folder and SSH workflows support focused discovery. Scheduled rescans and change monitoring help teams keep evidence current. Connector and detection-mode availability depend on the installed runtime, source, permissions and configuration.
Clear deployment boundaries.
Run on premises or in a customer-controlled cloud environment. Cloud-drive discovery still uses provider APIs and authorized access; deploying nearby does not remove service quotas. Optional AI must be configured for supported workflows. Argon supports compliance activities and does not itself certify legal compliance.
Deployment requirements